Preview
Coming 2027

oOsiris is a complete solution of smart badges and access points bringing GDPR-compliant biometric control to enterprises and governments. An end-to-end secure ecosystem featuring enrollment, credential issuance, authentication, management, revocation and replacement.
Passwords remain the weakest link: stolen or guessed credentials are the most common way in, in 22% of breaches (Verizon DBIR 2025), and centralized biometric databases keep getting breached. A leaked biometric cannot be reissued. In France, manipulation fraud reached €516 million in 2025, up 34% in a year (Banque de France, 2025 report): everything that can be dictated can be stolen.
oOsiris keeps biometrics in the user’s hand. The match runs inside the badge, and no biometric data ever leaves it: only a signed yes or no.
The badge proves who is at the door and that the holder is physically there, not only that a credential was presented. It works hands-free with oOsiris door readers (UWB), which connect to your existing access control panels (OSDP, Wiegand). There is no biometric database to breach.
Log in to workstations, VPNs and online services with FIDO2 passwordless authentication. The badge releases the key only after the holder’s biometric match.
Sign documents with a key that only the verified holder can release: each signature needs the holder’s code and biometric match.
A signed yes or no to a question such as “over 18?”, computed inside the badge. The date of birth is never revealed, and the check is anonymous, with double anonymity: the website never learns who you are, and no one learns which website asked.
The badge accepts a capture only from a GripID-certified camera: a deepfake injected into a video stream or a webcam is refused. Cameras add liveness detection against photos, videos and masks.
A cryptographic proof that a real person authorized an action: sign prompts and authorize AI agents.
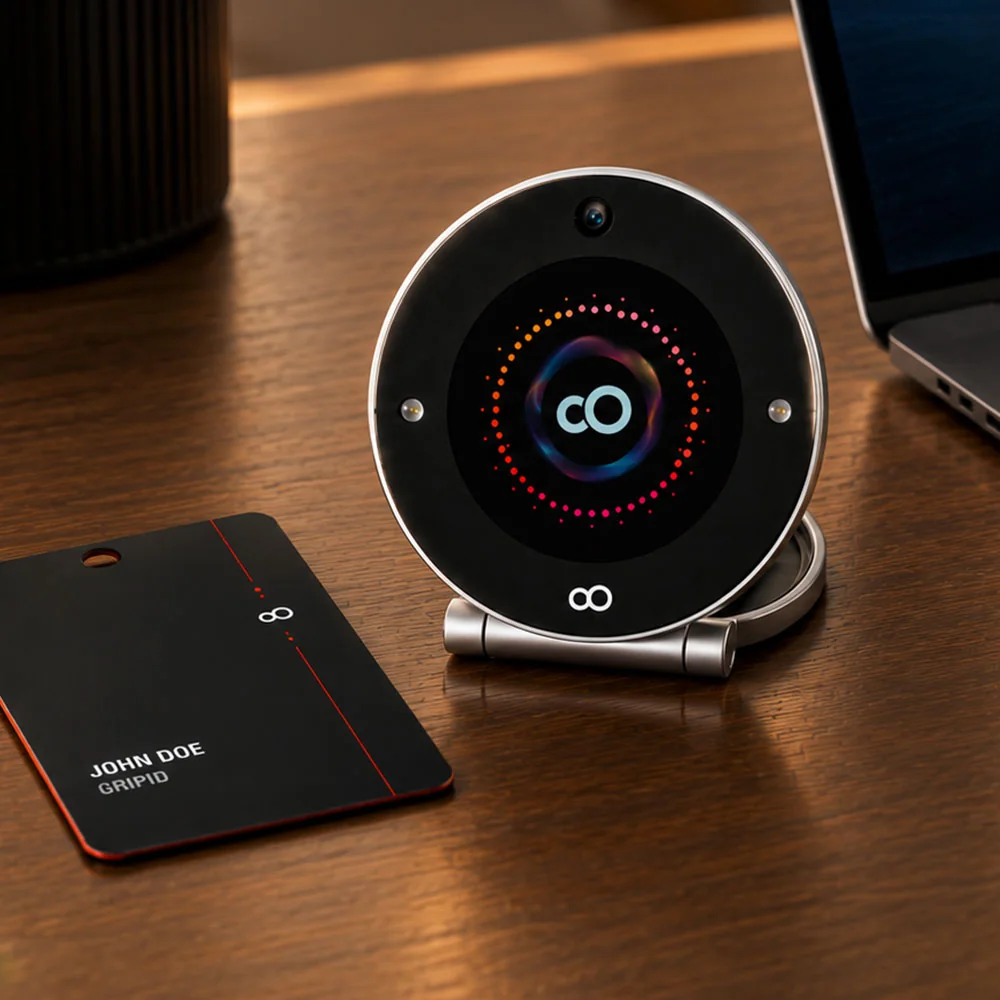
The badge holds the eID, the biometric template and the matcher. A smart camera captures the biometrics and sends it to the badge over a secure channel for local comparison. Biometric data is never stored or sent to a server.
How it works
The secure badge carries the digital identity (eID), the biometrics and the matcher. The smart camera captures the biometrics, sends them to the badge over a secure channel and receives a signed yes or no.
1
The user activates their badge in front of the smart camera.
2
The smart camera captures dual-iris and facial biometrics.
3
The smart camera sends the encrypted template to the badge.
4
Biometric match is performed inside the badge’s secure element.
5
The badge issues a one-time proof for that single operation.
6
The user can log in, open a door or sign a document.

Use case: banking
Every step is proven by smart camera biometric scan and match on card. The badge is owned by an employee, with their biometrics securely bound at enrollment.
1
Arrival: A face check at the door, for secure and easy access.
2
Workstation login: The session opens hands-free, no password.
3
Entering the order: The employee validates and signs.
4
Dual control: A second validator signs with their own badge and face.
5
Proof: A signed proof per validation, linked to its holder.
What disappears
What remains
The bank keeps control
For the bank’s customers
oOMS manages the oOsiris badges. It is built on the SDMS core, with the identity and badge layer on top.

Tell us about your project. From concept to field deployment,
our team is with you at every step.
Quality & Sovereignty
Solutions
Products
Company
The next step in digital trust.
Biometrics. Identity. Sovereignty.